Software security
Find and fix weaknesses before release.
New integrations and permissions can expand a system’s exposure. Review how data moves, who can access it, and which dependencies the system relies on.
What we deliver
A clear scope. Tangible work. A team ready for what comes next.
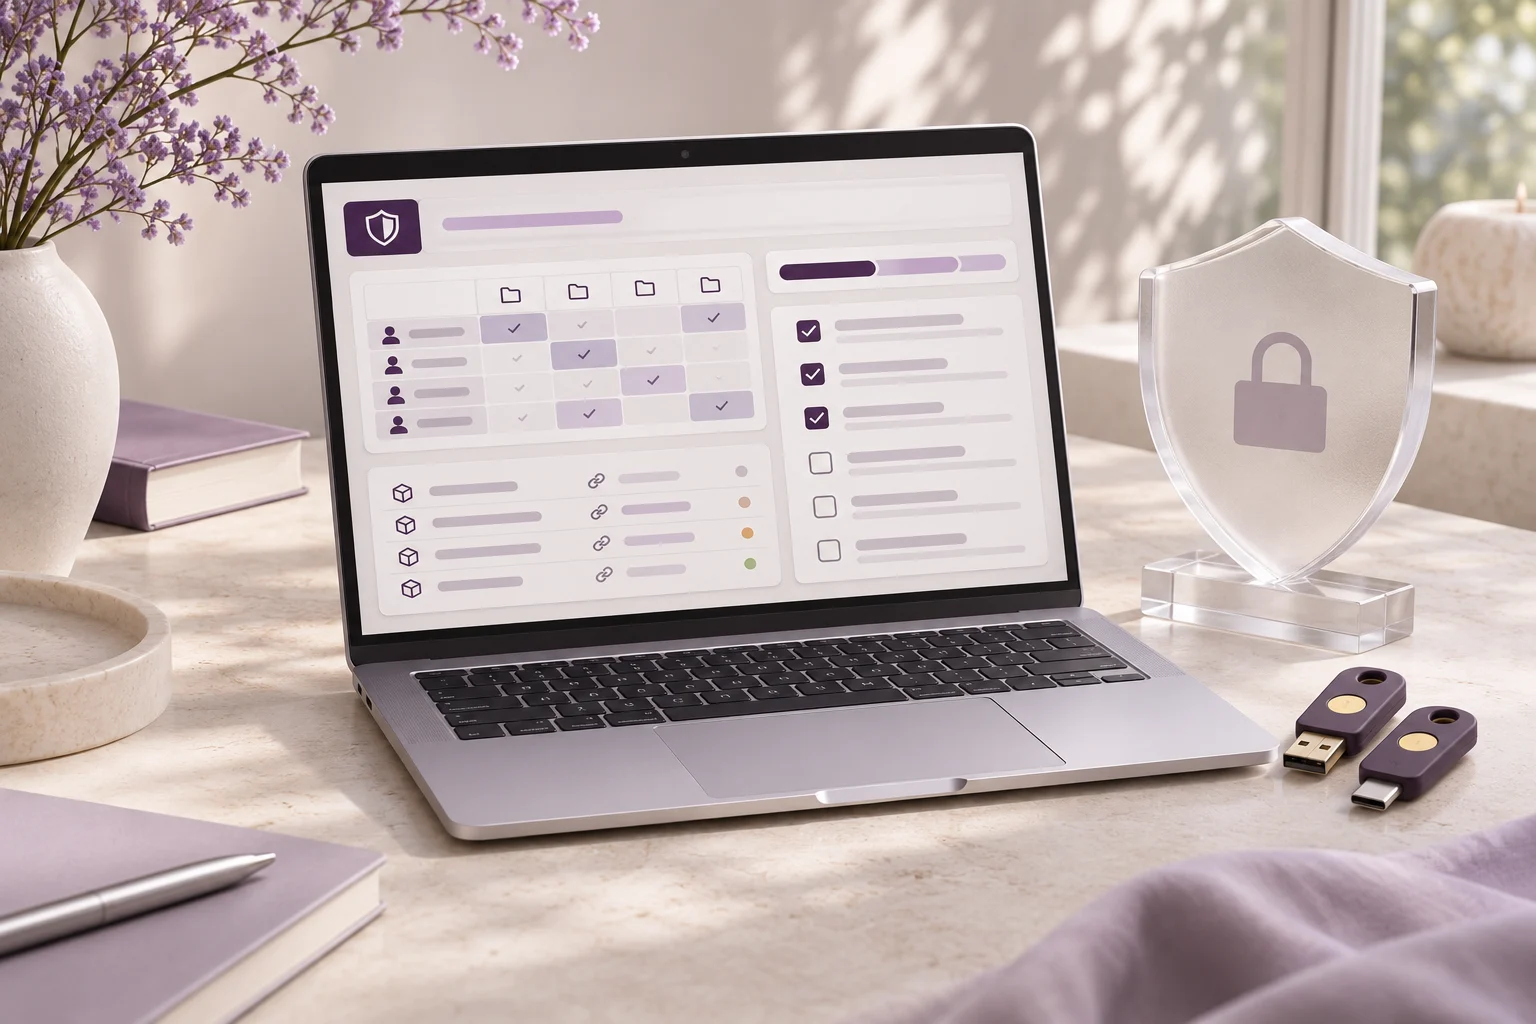
Architecture and access review
Dependency and configuration findings
Prioritized remediation and verification
How we deliver
From the first question to the next release, every step has a purpose.
Discovery
Define the problem, map constraints and agree on what the first release needs to prove.
Architecture
Map the systems and integrations, then decide where to build, connect or reuse.
Build & validate
Deliver in increments, review working software and build testing and security checks into the release process.
Launch
Plan deployment, monitoring and handover before the system goes live.
Ongoing support
Help your team operate the system, resolve issues and plan the next release.
Frequently asked questions
What does a software security review cover?
The scope can include trust boundaries, access rules, dependency risks, deployment configuration, and sensitive data flows.
When should we review security?
Review the design when adding permissions or integrations, and verify the implemented controls before wider rollout.
Can you review an existing application?
Yes. Identify the critical workflows, map who can reach them, and agree which environments and code are in scope.
How are findings prioritized?
Consider which users or systems are exposed, the possible impact, and the effort needed to reduce the risk.
What happens after fixes are made?
Verify the specific controls that changed and record any remaining risks or operational steps with the team.
Contact
What are you building?
Tell us what you’re working on and where you need engineering support.